Release Date: 2026-10-27
Potential False Positive Reporting in Portal
Please note: This change applies to automated scanning only. It does not apply to any managed subscriptions, including SWAT, Snapshot, Assure, DAST Expert, or fully manual tests. Findings from these services are validated by our security experts, and false positives are not reported to customers.
Network Host Assessments running in Portal have historically not reported Findings that Outpost24 considers to be at high risk of being false positives because of different criteria.
Amongst them;
-
Incomplete information
-
OS Distribution maintainers backporting software
-
Vulnerabilities not having clear indicators
Today Outpost24 is changing this behavior and letting the choice be with with the user of the platform such that they can have visibility into what Outpost24 has found that indicates that a vulnerability exists, but also what context indicates that the vulnerability is not relevant.
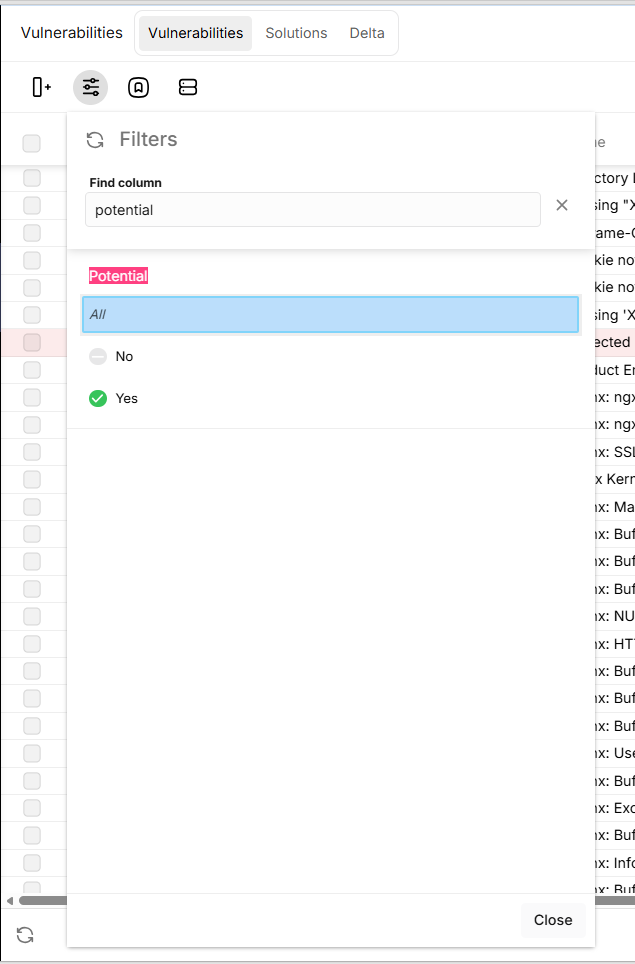
This will lead to an increase in Findings being reported, any may initially lead to some confusion. For now, the potential false positive attribute can be filtered on to see what you saw before, but omit the filter and you will see a fair bit more, but you need to be aware that they may have a high likelihood of being false positives.
Note that this change only affects Portal since Classic is already reporting potential false positives.
When will this matter?
The biggest impact will be seen on operating systems and distributions that are backporting software provided through their packaging system. The most notable one in recent time is the PHP vulnerability when running on some Linux distributions, especially older ones where specific advisories are no longer published.
Too many findings are reported!
This is a consequence of this shift in reporting strategy from Outpost24, but the system allows filtering in all layers after the Finding being created.
-
Reports can be filtered with View Templates.
-
Portal views can be filtered with View Templates.
What you are filtering on is the potential false positive on Findings. See Vulnerabilities for details.
Why is the status not updated?
We are also leaving the decision to consider these potential false positives as true false positives to the user. If you have a rule for what can be automatically assumed to be true false positives based on some criteria, it can possibly be automated via Automation Rules status transitions for when the Findings are created or seen.
See Auto Actions for details.